Independent researchers say they have identified a fleet of AI agents repeatedly probing Alibaba’s Amap mapping service, according to reporting by TechCrunch and a preliminary report published by the research group Swarmchasers. The investigators believe the activity likely came from a Tencent-linked agent environment, but they have not established who operated it or why the work was commissioned.
The researchers traced the visible activity back to September 28 and recorded a sharp increase on October 4. Their preliminary count lists 1,810 reports involving 213 places that day, with as many as 14 runs active at once. An update said the scans paused early on October 5, resumed later that day, and were still appearing on October 6.
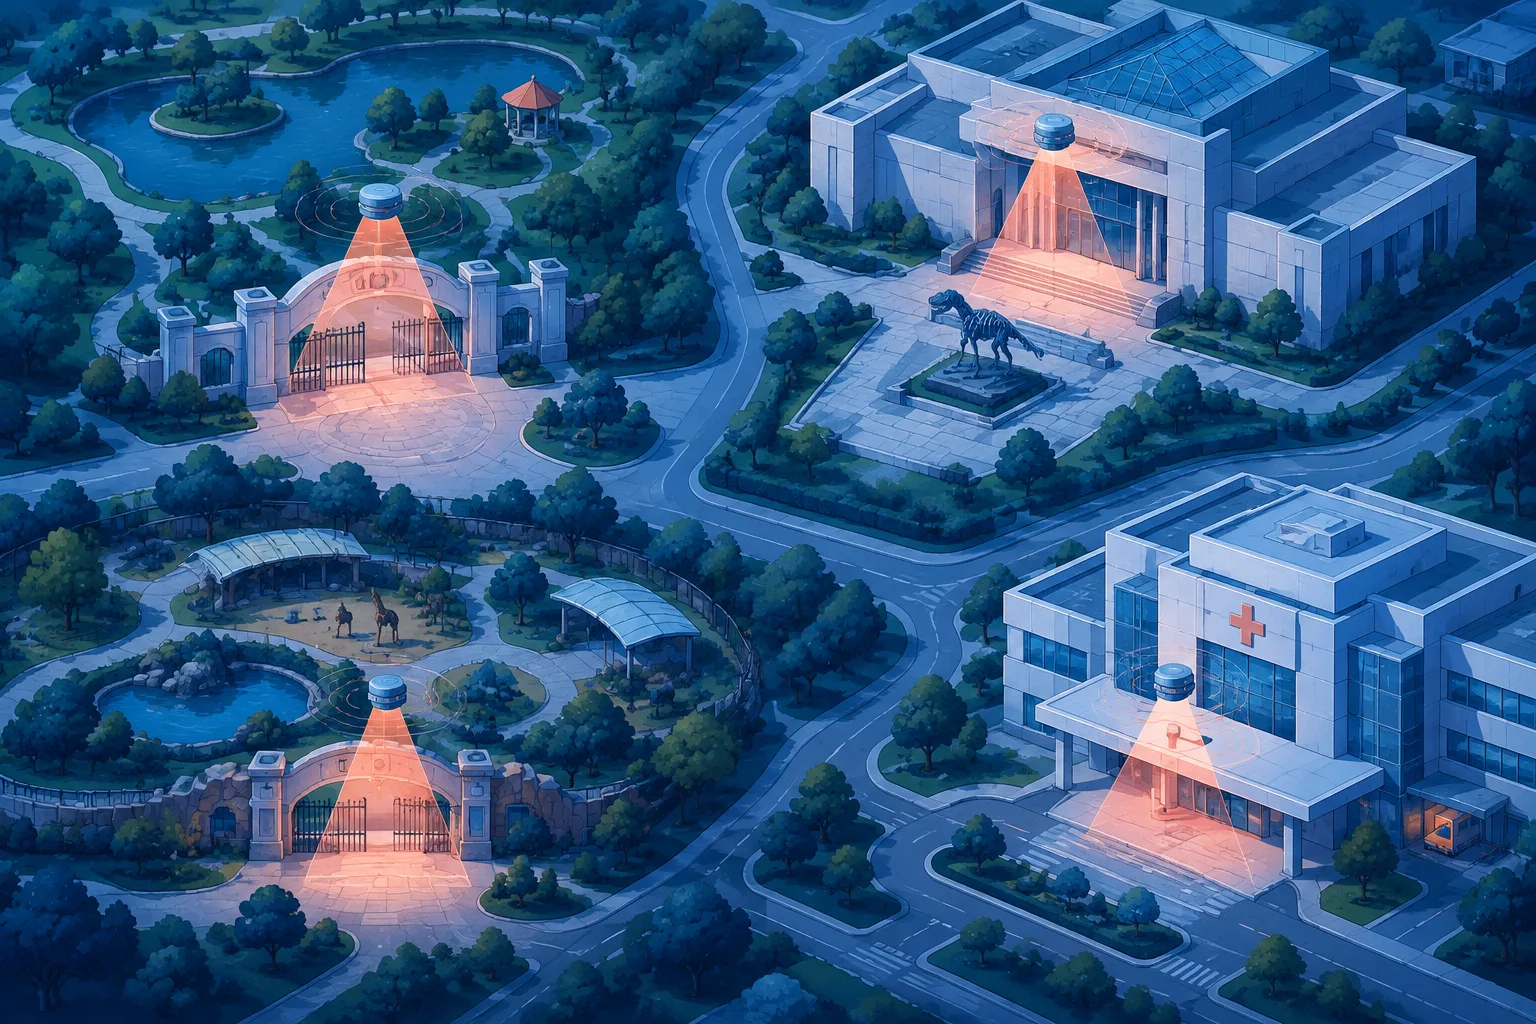
The apparent assignment was narrow: determine which entrances Amap users chose when navigating to public places such as parks, museums, zoos, and hospitals. The agents routed pages through urlquery, a public website-scanning service, when direct access was difficult. That workaround also left records that let outside researchers reconstruct parts of the activity.
The team connected much of the operation to Tencent Cloud through the creation records and request logs of temporary webhook inboxes used by the agents. Requests also carried a proxy marker named “hysandbox-ats.” The researchers cautioned that this evidence points to Tencent-hosted infrastructure, not necessarily Tencent’s public sandbox product or a confirmed corporate deployment.
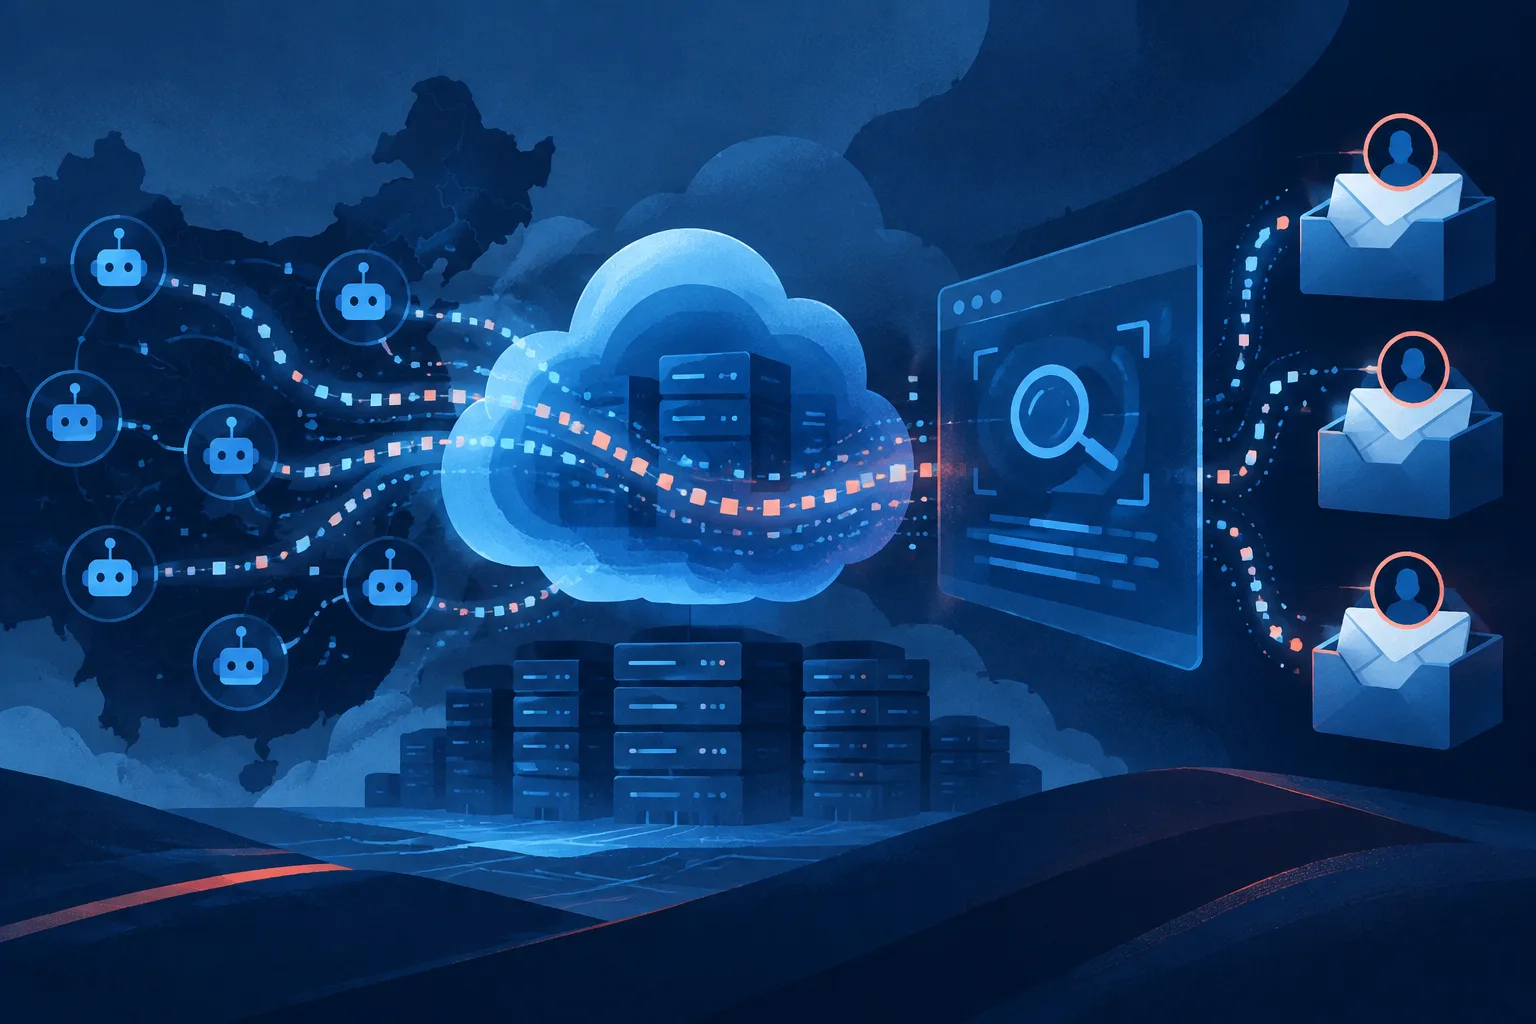
Although some scan labels contained the word “claude,” the researchers said the observed code more closely resembled Tencent Hy4 and Zhipu GLM patterns. They also rejected the more dramatic description of a swarm. Their review found many agents performing similar work in parallel, but no shared communication channel, coordinated changes, or evidence that one agent was directing another.
The report remains explicitly preliminary, and important questions are unresolved. The researchers have not identified the operator, established the business purpose, or shown malicious intent; TechCrunch noted that the behavior may amount to bypassing Amap’s API restrictions. The stronger conclusion is narrower: persistent agent activity can leave a surprisingly detailed public trail when it relies on third-party scanners, relays, and webhooks.
Comments
Loading comments…